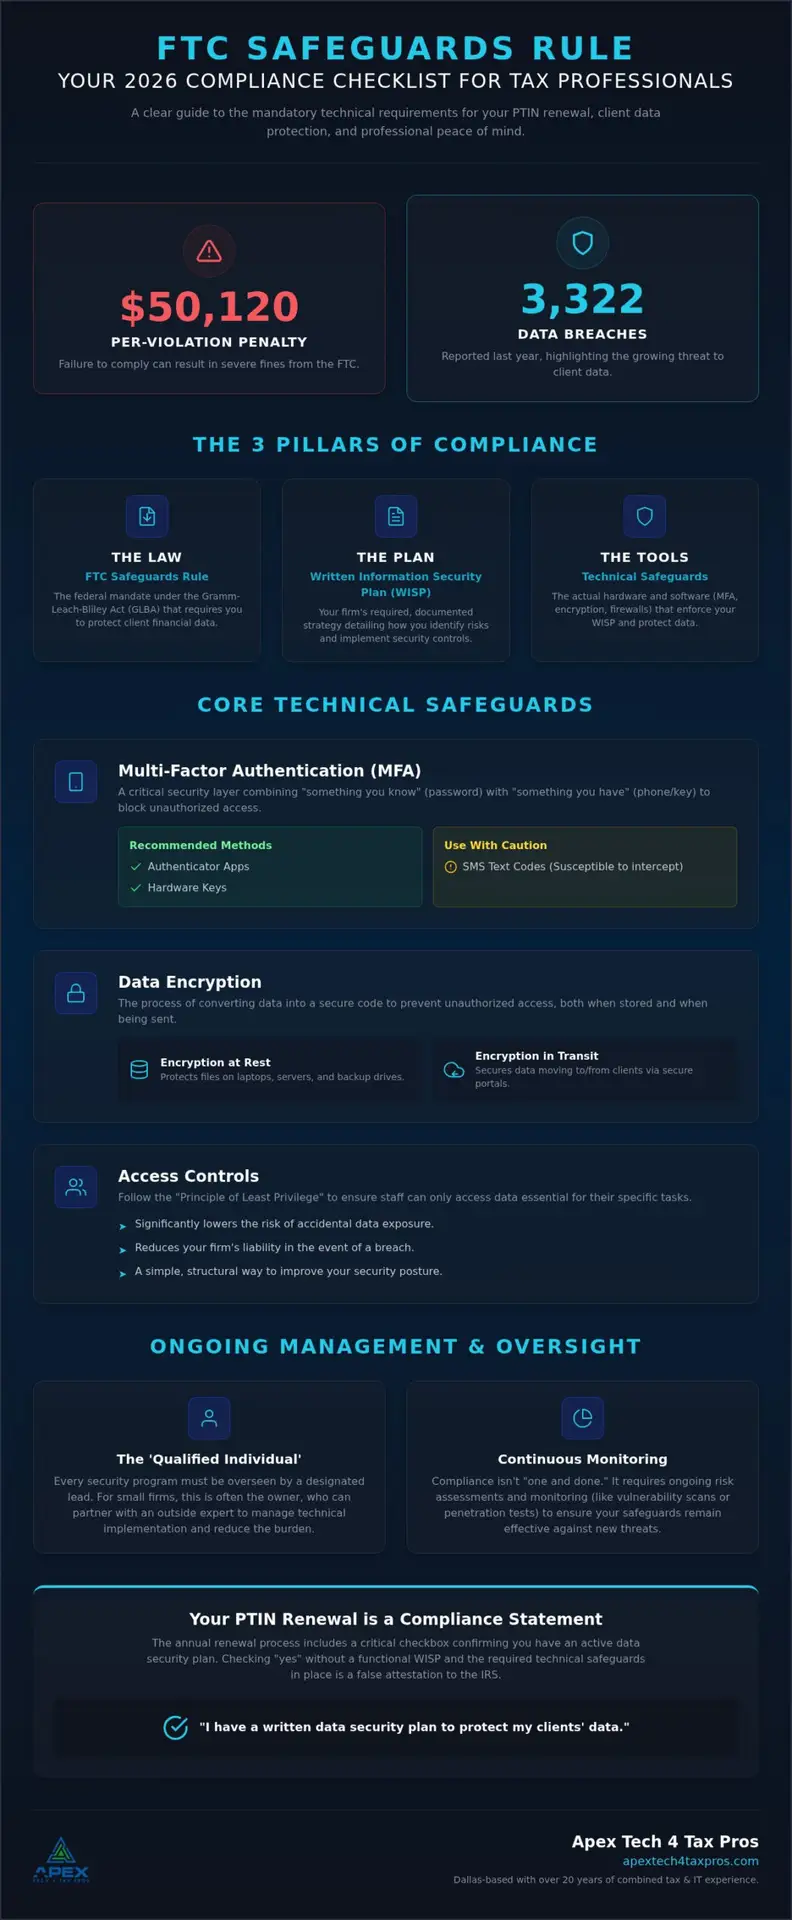
What if the most stressful part of your 2026 PTIN renewal isn’t the $18.75 fee, but the single checkbox asking if you’ve implemented a security plan? To meet current standards, you must satisfy specific ftc safeguards technical requirements such as multi-factor authentication, data encryption, and robust access controls. These aren’t just IT chores; they’re mandatory protections that keep your firm’s doors open and your client data safe from the 3,322 data breaches reported last year. I know that “technical requirements” often sounds like a code word for expensive, confusing, and time-consuming projects.
You’re a tax expert, not a systems engineer, and you shouldn’t have to be both just to stay compliant. This guide promises to simplify the process by showing you exactly which steps to take and how to implement them without the typical IT headache. We’ll cover everything from the “Govern” function in NIST CSF 2.0 to the documentation you need to avoid those $50,120 per-violation penalties. Let’s move your firm from a state of vulnerability to a state of secure, confident compliance.
Key Takeaways
- Identify the specific ftc safeguards technical requirements your firm must implement to remain compliant through the 2026 tax season.
- Learn why the distinction between your WISP and your technical security tools is the key to passing an IRS or FTC audit.
- Understand how to choose between vulnerability scans and penetration tests to protect your client data without overspending on generic IT services.
- Discover how a professional security framework provides relief from regulatory burdens while safeguarding your professional reputation.
What are the FTC Safeguards Rule technical requirements for 2026?
The FTC Safeguards Rule requires tax preparers to implement specific technical controls including multi-factor authentication (MFA), data encryption, and continuous access monitoring. These ftc safeguards technical requirements fall under the broader umbrella of U.S. financial privacy laws, specifically the Gramm-Leach-Bliley Act (GLBA). It’s helpful to distinguish between three core elements: the Safeguards Rule is the federal law, the WISP is your written strategy, and your technical tools are the actual armor protecting client data. By 2026, the standards have become highly prescriptive. You can’t rely on vague promises of security; you need documented proof that every requirement is active and monitored.
Who is covered by the FTC Safeguards Rule?
Many independent preparers and small office owners assume these rules only apply to large banks. However, under FTC jurisdiction, any business significantly engaged in financial activities is a “financial institution.” This includes every CPA and tax professional with a PTIN. There’s a direct nexus between your annual PTIN renewal and your compliance status. When you sign that renewal, you’re attesting that a Customized WISP is already in place and functioning within your office.
The ‘Qualified Individual’ requirement for small firms
Every security program must be overseen by a designated “Qualified Individual.” For a solo practitioner, this role often falls on the owner by default. You don’t need a computer science degree to fill this position, but you do need to be responsible for the program’s oversight. Many firms choose to designate an internal lead while partnering with an outside expert to handle the complex technical implementation. This ensures the ftc safeguards technical requirements are met without pulling you away from your core tax work. This collaborative approach provides a relief from the burden of self-managing complex IT infrastructure.
What are the core technical safeguards for MFA, encryption, and access control?
Building on the regulatory context we’ve discussed, the actual implementation of ftc safeguards technical requirements starts with controlling who sees what. Using the “principle of least privilege” isn’t about a lack of trust; it’s about reducing your workload and liability. By ensuring staff only access the specific tax files needed for their current tasks, you significantly lower the risk of accidental data exposure. This simple structural change provides an immediate sense of relief, knowing your office isn’t a wide-open digital floor plan where every file is vulnerable to a single compromised password.
How do I secure my data in transit and at rest?
Encryption is essentially a digital lock for your data. You need to protect information “at rest”—meaning files sitting on your laptop, server, or backup drives—and “in transit” as it moves between you and your clients. Instead of relying on vulnerable email attachments, many of our colleagues now use secure client portals to handle sensitive tax documents. This keeps data encrypted from end to end. For your physical office, setting up a Secure Office Network helps isolate this sensitive traffic from guest Wi-Fi or generic web browsing. If you’re feeling overwhelmed by these choices, a professional it assessment can pinpoint exactly where your encryption needs a boost.
How should I implement Multi-Factor Authentication (MFA)?
MFA is simply a “something you know plus something you have” security layer that provides a powerful barrier against unauthorized access. While any MFA is better than none, the current standards strongly favor authenticator apps or hardware keys over SMS text codes. SMS is susceptible to intercept, whereas an app on your phone provides a much more secure handshake. You should enable this for your tax software, professional email, and any cloud storage accounts. It’s a straightforward step that ensures your firm meets federal standards while allowing you to focus on serving your clients with the confidence that their most sensitive records are protected by more than just a password.
How do I implement continuous monitoring and risk assessments?
Compliance isn’t a “one and done” task; it’s more like a recurring health check for your firm. To meet the ftc safeguards technical requirements, you need a clear picture of what’s happening on your network at all times. This starts with a detailed hardware inventory of every laptop, tablet, and server that touches client data. Once you know what you have, you can monitor for unusual data movement or unauthorized access. It’s about being proactive rather than reactive, which takes the panic out of security. While large firms might have 24/7 security teams, smaller offices can achieve this through a mix of automated tools and periodic reviews.
- Vulnerability Scans: These automated tools are like a digital locksmith checking your windows for cracks.
- Penetration Tests: This is a more hands-on approach where a pro tries to find ways into your system, just like a real attacker would.
How do I conduct an annual IT assessment?
A thorough IT assessment is the best way to identify “reasonably foreseeable” risks to your clients’ data. You’ll look at your software patch levels and hardware age to see where you’re vulnerable. When you link these results to your Written Information Security Plan (WISP), you create a solid trail of documentation for any auditor. If you want to stop guessing and start knowing where your office stands, book a professional assessment today to get a clear, actionable report. This process bridges the gap between your tax preparation expertise and the technical infrastructure you rely on every day.
Why is personnel training considered a technical safeguard?
The FTC views cybersecurity awareness training as a technical defense because your team is your front line. Attackers often use AI-generated phishing emails that look exactly like IRS notices or client tax documents. Training your staff to spot these tells is just as effective as any firewall. When your team knows what to look for, you gain the relief of knowing your human firewall is just as strong as your digital one. This ongoing education ensures that your security culture stays as current as your tax knowledge.
How can I simplify compliance using WISPs and professional support?
Integrating all the ftc safeguards technical requirements into a cohesive system can feel like a full-time job. This is where your Written Information Security Plan (WISP) moves from a regulatory burden to an operational asset. It acts as the central nervous system for your firm’s security, documenting every protocol from your firewall settings to your data disposal habits. Instead of treating security as a series of disconnected tasks, a Customized WISP provides the structure you need to demonstrate compliance to the IRS and FTC with total confidence.
How do I develop a Written Information Security Plan (WISP)?
To satisfy the 2026 standards of IRS Publication 4557, your plan must be more than a generic printout. It needs to name your ‘Qualified Individual,’ list your specific hardware inventory, and outline your exact response plan for a data breach. A tailored plan proves you’ve performed the due diligence required by federal law. While generic templates are a starting point, they often fail under the scrutiny of an actual audit because they don’t reflect how your specific office operates. A customized approach ensures your documentation matches your actual day-to-day security practices.
When should I seek professional assistance?
You didn’t become a tax expert to spend your nights configuring servers. Our Seasonal subscription ($649.99) and Yearly subscription ($1,099.99) offer a relief from this technical burden by providing a free customized WISP and expert guidance. We leverage over 20 years of combined tax and IT experience to bridge the gap between financial services and cybersecurity. While our sister company, APEX Tax Solutions, handles high-stakes tax resolution and preparation, we focus on the technical side of the house. This partnership ensures that while they protect your clients’ financial standing, we protect the data that makes it possible. If you’re ready to simplify your office, email info@at4tp.com to start your journey toward secure compliance.
Securing Your Firm’s Future for 2026 and Beyond
Meeting the ftc safeguards technical requirements doesn’t have to be a source of constant anxiety. By implementing strong MFA, encrypting data at rest and in transit, and maintaining a live Written Information Security Plan, you protect your clients and your professional standing. These steps move you away from the fear of audits and toward a state of demonstrable security. It’s about building a resilient practice that can withstand the evolving threats of the digital landscape.
At Apex Tech 4 Tax Pros, we bring over 20 years of combined tax and IT experience to help independent preparers navigate these federal mandates. Our Seasonal and Yearly subscriptions even include a free customized WISP to get you started immediately. We’re trusted by tax office owners nationwide because we understand the specific pressures of your industry. If you’re ready to cross compliance off your to-do list, it’s time to take action. Book a WISP Assessment with Apex Tech 4 Tax Pros today. You’ve worked hard to build your practice; let’s work together to keep it safe.
Frequently Asked Questions
Is the FTC Safeguards Rule the same thing as an IRS WISP?
No, these are two different but related concepts. The Safeguards Rule is the federal law that mandates data protection for financial institutions. The Written Information Security Plan (WISP) is the specific document required by both the FTC and the IRS to prove your firm has a security strategy. Think of the Rule as the legal requirement and the WISP as your roadmap for following it.
Do I really need MFA if I am a solo tax preparer working from home?
Yes, multi-factor authentication is a mandatory requirement for every tax professional, regardless of firm size or location. The FTC updated its rules to remove exemptions for small businesses regarding MFA implementation. Whether you work from a large corporate office or a spare bedroom, you must use MFA for any individual accessing systems that contain sensitive customer information to stay compliant.
What are the penalties for non-compliance with the FTC Safeguards Rule in 2026?
Non-compliance carries heavy financial and professional risks. In 2026, civil penalties can reach up to $50,120 per violation. These amounts are adjusted for inflation and can add up quickly if an auditor finds multiple security gaps. Additionally, the IRS has the authority to suspend your EFIN or PTIN, which effectively prevents you from filing tax returns and operating your business legally.
How often do I need to update my technical risk assessment?
You must update your risk assessment at least annually to remain in line with ftc safeguards technical requirements. You should also perform a new assessment whenever you make a significant change to your business. This includes switching software providers, adding new hardware to your network, or moving files to a cloud-based system. A current assessment ensures your WISP reflects your actual office environment.
Does the FTC Safeguards Rule require me to encrypt all my emails?
The Rule requires you to encrypt all customer information while it is in transit over external networks. Standard, unencrypted email is generally not secure enough to meet this federal standard. Most tax professionals meet this requirement by using secure client portals for document exchanges. This ensures that sensitive data stays protected from the moment it leaves your computer until it reaches your client.